by DNSFilter on Jul 6, 2021, 12:00:00 AM
Just before US offices closed for the Fourth of July holiday, the MSP vendor Kaseya was hit by a huge ransomware attack. The organization behind the attack is REvil, a Russian-linked Ransomware-as-a-Service operation that first surfaced in May 2020. In 2021, they have been attached to a number of high-profile attacks. This breach is still ongoing, but we want to alert our customers to the actions that we have taken at DNSFilter to best secure our customers.
We want to reiterate that if you are a Kaseya customer to follow their advice:
“Our guidance continues to be that users follow Kaseya’s recommendation to shut down VSA servers immediately, to adopt CISA’s mitigation guidance, and to report if you have been affected to the IC3.”
Initial Domain Flagged
At 3:56 p.m. ET on July 2, DNSFilter categorized the first known URL as malware after it was first posted at roughly 3:19 p.m. ET: decoder[dot]re
Prior to our categorization of this domain, there was no traffic to this domain on our network.
Config file with over 1,000 domains disclosed
Early on July 3, a config file was released for the Kaseya attack that included a list of over 1,200 command and control domains. As of 3:58 a.m. ET on July 3, DNSFilter is categorizing all of these domains as malicious.
To ensure you’re protected from these domains sending DNS queries from your system, ensure you have the following DNS threat protection in place (at a minimum) on our network:
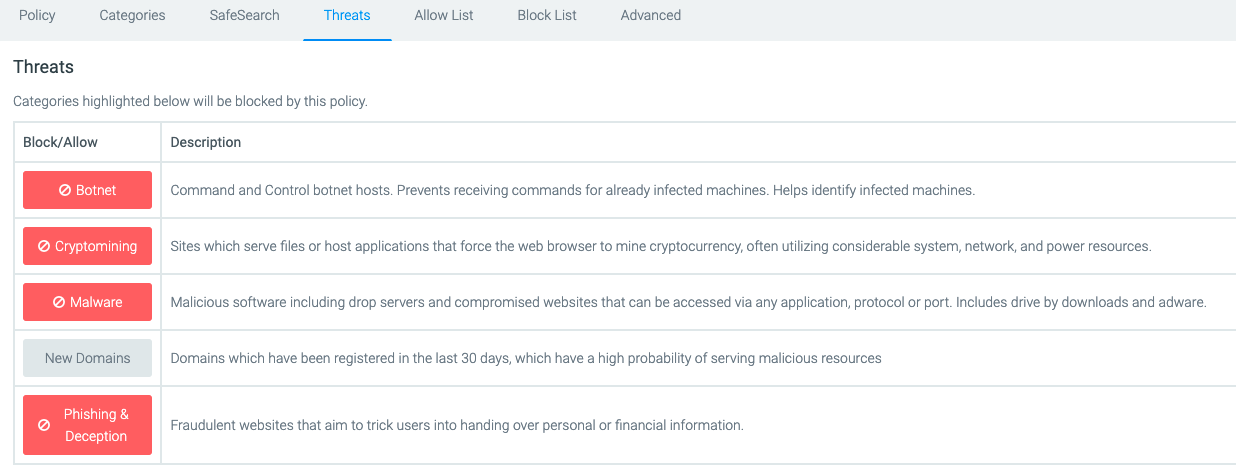
As more information is released or we have additional updates related to actions we are taking at DNSFilter to protect our customers, we will update this blog post.
Update on July 9, 2021: We have shared more information about the CNC domains used in the Kaseya ransomware attack.
 What Is DNS-First Security?
DNS-first security is an approach that makes the DNS lookup the first security decision point. Because every connection starts with a DNS request, a DNS-first platform decides whether to allow or block at that lookup, before a connection forms.
 LUMINATE by DNSFilter™ and the Bet We Made 11 Years Ago
When I co-founded DNSFilter in 2015, we made one bet: stop threats at the very first moment, before anything happens. Today, we're taking that bet further than we ever have.
 We Built One Engine Instead of Five: Inside LUMINATE by DNSFilter™
Today LUMINATE by DNSFilter™ launches from the Nasdaq MarketSite in Times Square. My product and engineering teams built it, and I want to share how, because the decisions we made along the way explain why it works the way it does.


